NEURIXA Proxy
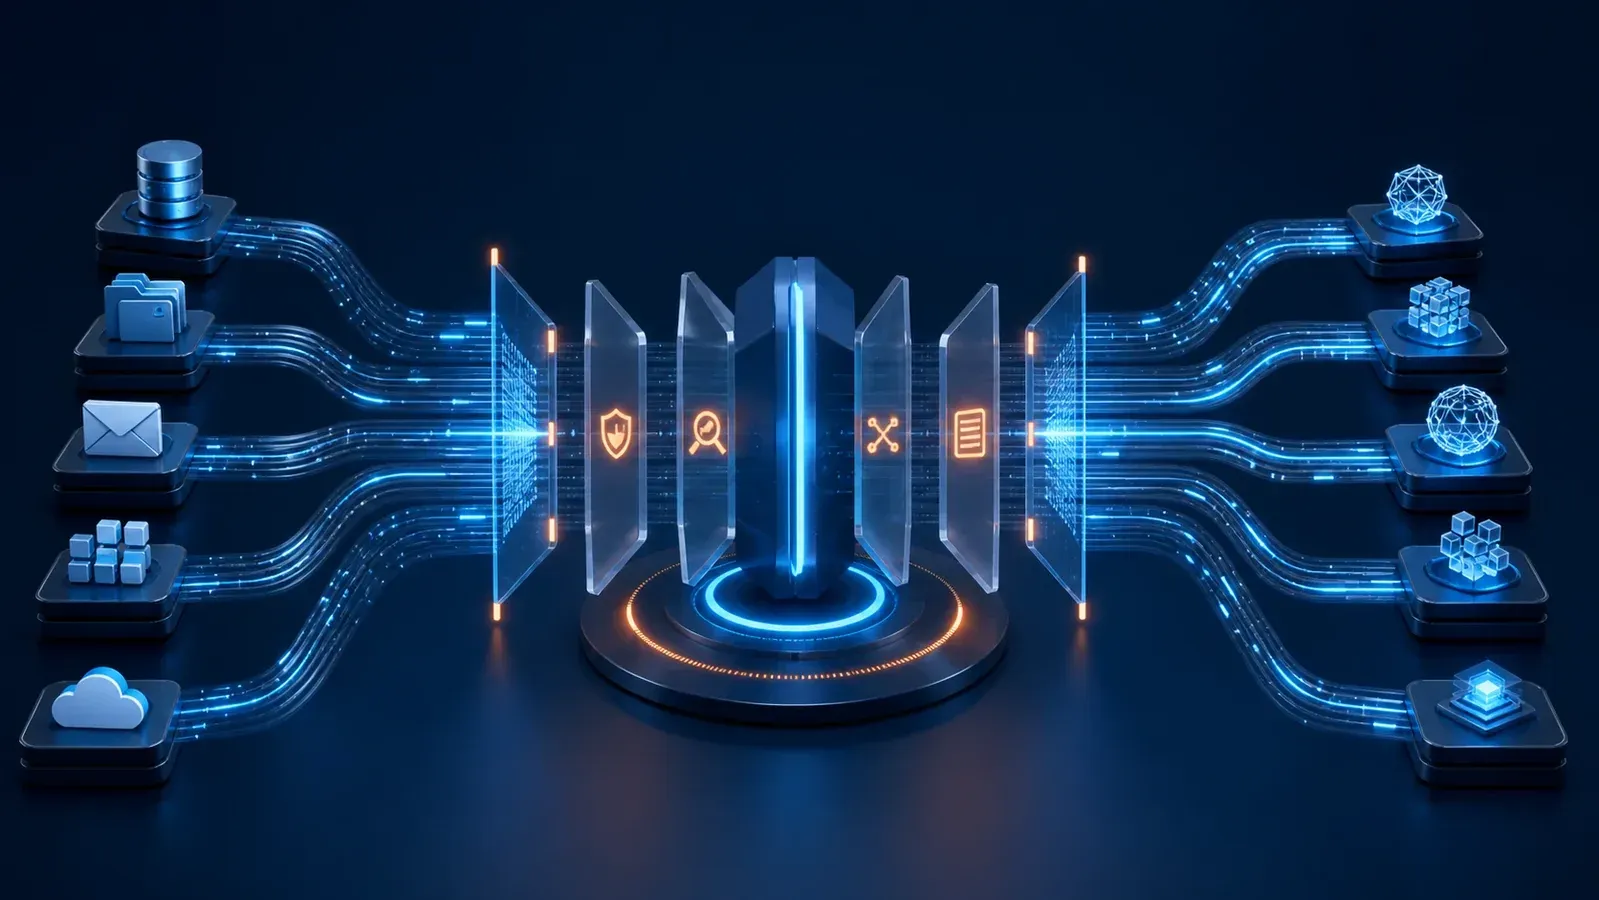
Govern organisational AI access through one controlled and traceable gateway.
As AI services spread across an organisation, individual applications and users may connect to different providers with inconsistent security, data-handling, model and cost controls. Direct access makes it difficult to understand what information leaves the organisation, which model processed it and whether the request followed an approved policy.
NEURIXA Proxy is designed as a control and evidence point for organisational AI traffic. It is more than a conventional network forwarder: it connects identity, permissions, data rules, model selection, operational limits and transaction records.
Why a central AI gateway matters
Without a common control point, every AI-enabled application must implement its own safeguards. Policies can diverge, provider changes become difficult to manage and investigations may lack a complete transaction record.
The Proxy approach separates applications from model providers while allowing organisational rules to be applied consistently.
How the capability works
Identify the request
An AI transaction can be associated with the authorised user, application, project or organisational context from which it originated.
Apply access and data-handling rules
Requests can be checked against permissions, data classifications and applicable handling requirements. The objective is to prevent unapproved use and reduce unnecessary exposure of personal, confidential or sensitive information.
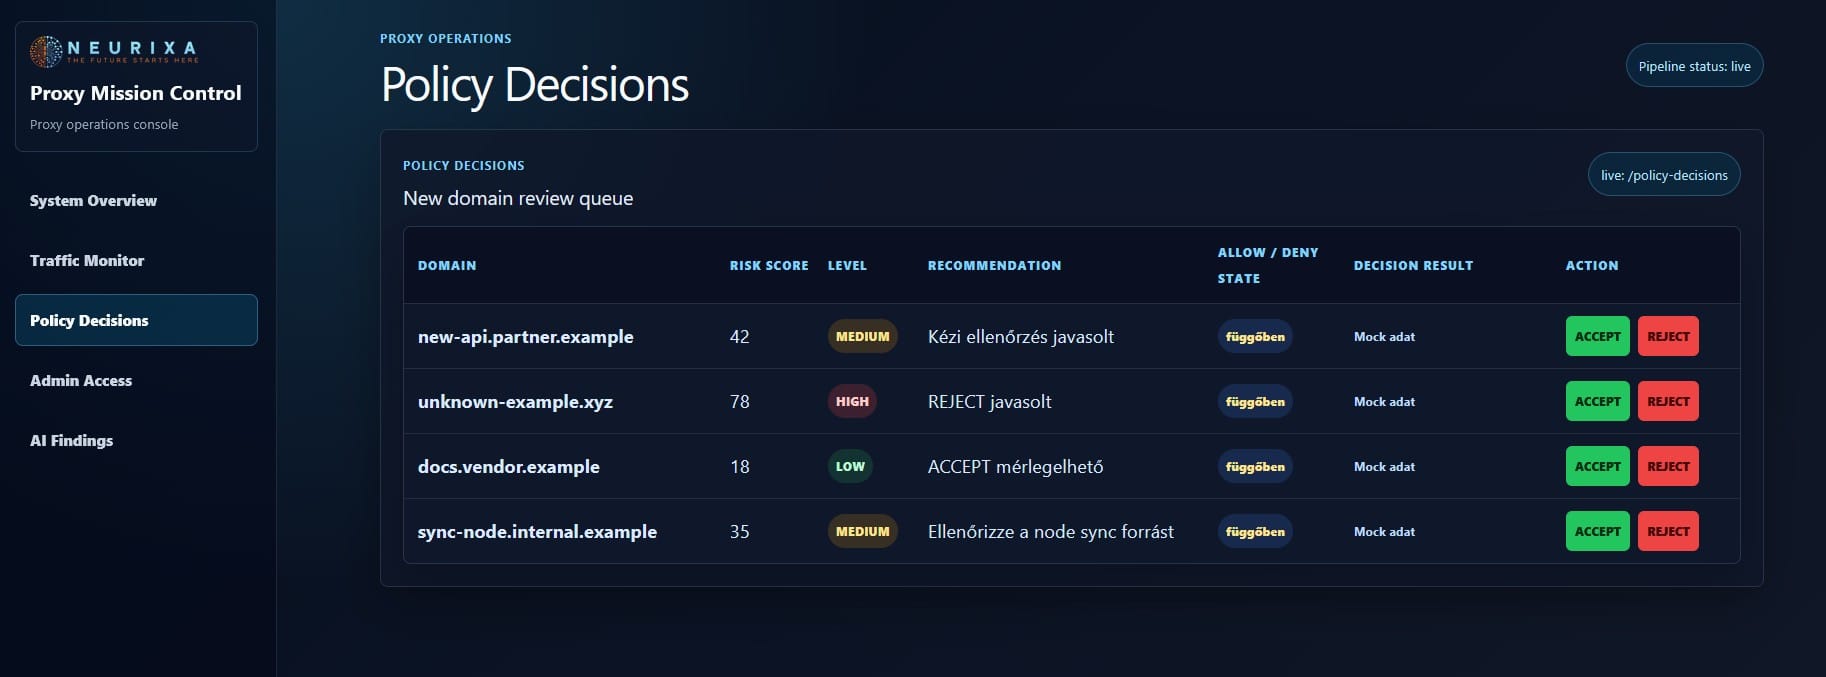
Actual NEURIXA Energy Control workspace shown with demonstration data.Route to an approved model
The selected model or provider can depend on the task profile, required capability, data policy, risk, availability and cost constraints. Routing is a governed decision rather than an invisible application choice.
Record the transaction
Relevant request, routing, policy and outcome information can form a traceable transaction record. This supports monitoring, troubleshooting, cost interpretation and security investigation.
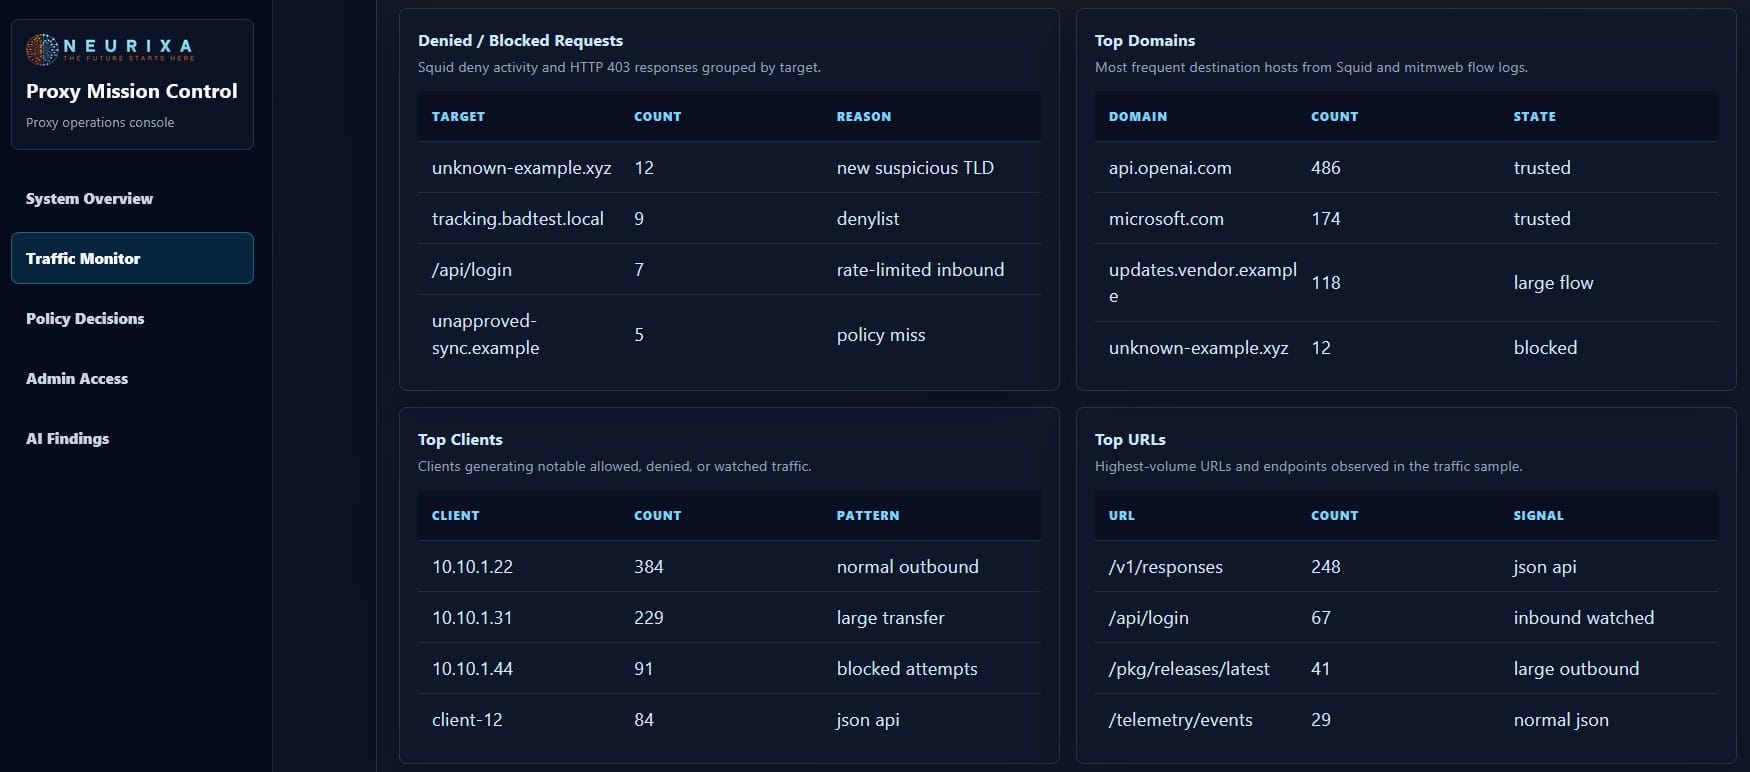
NEURIXA Energy Control dashboard showing daily load, intraday prices, market spreads, storage state and advisory trends.Example: controlled external-model use
An internal application needs language assistance for a policy summary. The request contains a mix of public content and internal material.
The Proxy can support identification of the application and user context, application of the relevant data rule and selection of an approved model route. The resulting record can show which controls were applied and which service processed the permitted request.
Typical applications
- central access to approved AI services;
- model and provider governance;
- data-minimisation and handling controls;
- project or customer separation;
- AI usage and cost visibility;
- transaction evidence for security and audit workflows.
Connected security
The Proxy does not replace SIEM or SOC capabilities. It enforces AI-use rules and emits relevant evidence; the SIEM can collect and correlate events, while the AI SOC can build investigation context. The three roles remain distinct.
Human and policy control
The gateway does not independently define organisational policy. Authorised owners remain responsible for permitted models, data classifications, routing rules, exceptions and consequential response decisions.